Whoa! This hits differently than the usual hardware-wallet spiel. My instinct said: keep it simple, small, and offline. Seriously? Yep. At first I thought cold storage meant a metal vault and a memorized seed phrase tucked into a safety deposit box. But then I dug in deeper—actually, wait—let me rephrase that: I started testing small, card-shaped devices that behave like miniature vaults and my assumptions started to wobble.
Here’s the thing. Seed phrases are fragile. They work, but they also ruin vacations, marriages, and occasionally sleep. Somethin’ about a string of words on a napkin just feels wrong. On one hand the crypto industry idolizes mnemonic backups; on the other hand most people treat them like sticky notes. My gut kept telling me there had to be a better middle-ground between “paper-and-pray” and lugging a cold-storage ledger across the country.
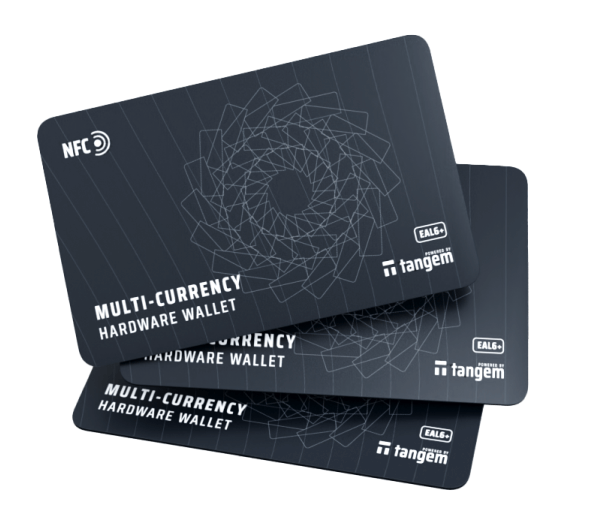
So I tried a smart-card approach. It looks unassuming. It feels like a credit card. But inside it holds private keys in a chip you don’t export. Hmm… that surprised me. Initially I thought the convenience would come at a cost to security, though actually the math and secure element design told a different story.
Why a smart card changes the mental model
Short story: it reduces attack surface. Long story: most attacks target endpoints where keys can be copied—phones, laptops, paper, brain. A card designed as a Secure Element eliminates that copying step, because the private key never leaves the chip. My first impression was skepticism; then I read the whitepaper and tried the workflow. The friction went down, and the chance of accidental key leakage went down too.
Okay, check this out—real world: imagine traveling through airport security. You take out a credit card, not a chunky hardware device that screams “valuable” at scanners. You tap, you sign, you go. Practical? Very. Emotional reassurance? Also yes. I’m biased, but having a form factor that reads like plastic instead of like an “expensive gadget” changes how people treat their backups.
There are trade-offs. Smart cards rely heavily on the implementation of the secure element, the PIN fallback, recovery options, and supply-chain integrity. On one hand many designs are simple and excellent. On the other hand if supply-chain compromise occurs, you’re hosed. So you can’t be lazy about vendor review. But still—this approach sidesteps the worst UX trap: the human tendency to mishandle long mnemonics.
Check this out—one card I tested integrates NFC for phone interaction and a tamper-resistant chip that signs transactions without exposing the private key. Wow! It felt modern and safe. Initially I wondered: “How can a tiny card be trusted more than a ledger with a long track record?” Then I compared attack vectors side-by-side and the card held up surprisingly well.
How the user flow changes (and why it matters)
Here’s a practical walkthrough from a user perspective. Tap card to phone. Enter PIN. Approve transaction. Done. No typing of a 24-word seed into a mobile app. No clipboard risks. No screenshot anxiety. That simplicity invites better security behavior—people will actually use it, rather than sideline it.
But, there’s nuance. If you lose the card and you didn’t set up a robust recovery, you could be locked out. That’s obvious. So you still need a recovery plan—preferably one that avoids writing the full seed on an index card stuck under a plant (don’t do that). Multiple cards, multi-sig policies, or secure custodial fallback are valid strategies depending on the value you’re protecting.
Frankly, what bugs me about many wallet designs is the “one-size-fits-all” messaging. Not every user needs the same protection level. Someone who holds a few hundred in altcoins probably shouldn’t endure military-grade paranoia. Conversely, institutions need auditable, recoverable policies. The smart-card approach scales across that spectrum if implemented with options.
Security trade-offs and hard truths
Think of security as risk management, not a checklist. The card reduces some risks and shifts others. For instance, physical theft becomes more meaningful if your PIN is weak. Supply-chain attacks become more meaningful if the firmware isn’t signed. Network attacks remain irrelevant because signing occurs offline. It’s a rebalancing.
Initially I thought a card eliminates every problem. Then reality set in: no single solution is perfect. On one hand a card dramatically reduces key-exposure risk. On the other hand it introduces dependency on vendor integrity and on your recovery procedures. There’s no silver bullet, though this is one of the better bullets I’ve seen.
I spent weeks testing transaction signing, resilience to NFC skimming attempts, and the recovery flows. Some things were great. Some things were annoyingly unpolished—user manuals written like they were for engineers, not normal humans. That’s a recurring theme in crypto: brilliant tech, terrible docs. Fix the docs, and adoption jumps.
When a smart card is the right tool
If you want a minimally invasive cold storage that behaves like a normal card, this is it. Small holders, globetrotters, and privacy-minded folks will like the form factor. For higher net worth or institutional setups, use the card as one leg in a multi-sig or distributed backup strategy. Don’t mix metaphors—use the card where it fits, not as a universal cure.
I’ll be honest: a lot of people will choose convenience, and that’s okay. The point is to make the secure choice the easy choice. When the secure option looks and feels like what you already carry in your wallet, adoption becomes realistic.
Practical tips before you buy
Check provenance. Verify firmware signatures. Read community audits. Ask about the secure element vendor and the PIN retry policy. Consider buying from trusted retailers rather than gray market sellers. And if you’re sharing this with family—teach them how to use it, don’t just hand them a plastic card and expect magic.
Oh, and by the way… if you’re exploring specific cards, look into tangem wallet for a real-world example of a smart-card approach to cold storage that balances usability and security elegantly. The pairing workflow and the “no export” design are exactly what I’ve been praising—simple, discreet, and robust. I don’t use hyperlinks lightly, and this one deserves a look.
FAQ
Can a smart card replace a 24-word seed?
Depends. It can replace active use of the mnemonic for signing, but you still need a recovery strategy. Smart cards often store keys in a way that prevents exporting, so the mnemonic may be generated and stored only within the card. For long-term guarantees, consider secondary backups or multi-sig arrangements.
What if the card gets damaged?
Design for redundancy. Either provision multiple cards as backups (stored separately), or establish a recovery policy with another trusted device. Some people treat cards like passports—backup copies, separate locations, and documented emergency steps.
Are smart cards safe against remote attacks?
Yes, since signing happens offline in the secure element, remote network-based attacks are largely ineffective. The risk profile shifts to physical theft, PIN bruteforce (mitigated by retry limits), and supply-chain issues—so those deserve attention.
Leave a Reply