Whoa! I remember the first time I slid a smart card into a reader and thought, “This could change things.” My instinct said it would feel less clunky than a seed phrase on paper, and honestly that gut feeling stuck. Initially I thought hardware wallets were all bulky devices, yet the idea of a minimalist, card-shaped key made sense in a way that surprised me. On one hand it’s elegant; on the other, there are real trade-offs that deserve attention.
Really? The convenience is deceptively powerful. For many people, handling keys needs to be fast and frictionless. Something felt off about the obsession with tiny screens and complex menus—users want simple habits, not crypto yoga. I’m biased, but I believe physical form-factor matters a lot when security meets everyday use.
Here’s the thing. Smart-card wallets (the kind that act like a tamper-resistant chip in a credit-card shell) compress a lot of tech into a low-profile package. They store private keys in secure elements, sign transactions offline, and pair with phones via NFC or Bluetooth, depending on the model. These cards trade visible bells and whistles for stealth and durability, and that trade sometimes makes them a better fit for people who hate fuss. On the practical side, they reduce attack surface—no keyboard, no touchscreen, just a passive secure chip that won’t leak your mnemonic to a compromised app.
Hmm… it isn’t perfect though. If you lose the card, you still need a recovery plan. And a smart card’s user flow can freak out someone used to custodial apps. Actually, wait—let me rephrase that: the real question is whether you accept a physical-token mindset instead of a passphrase-first mindset. On balance, I think most everyday users will prefer a card they can tuck into a wallet or phone case.
Simpler UX, strong security—how that balance plays out
Okay, so check this out—security is multi-layered here. Short sentence, but meaningful. Many smart-card solutions use certified secure elements, and the private key never leaves that chip. That means even if your phone is fully pwned, an attacker can’t extract the key through software alone. On the flip side, some cards have limited firmware update pathways, which can be a maintenance headache over years.
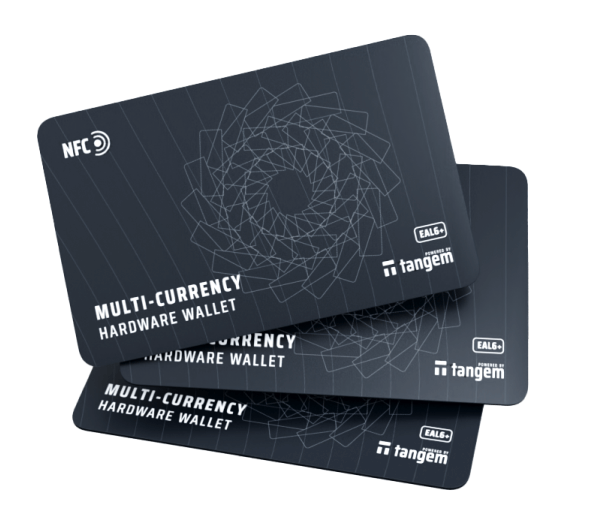
I’m often asked which brands I trust. I’ll be honest: no vendor is perfect, but some design choices stand out. For folks seeking a minimalist, durable option, the tangem hardware wallet card is worth a look because it blends usability with offline key storage on a card form factor. It’s a practical choice for people who want something less intimidating than traditional metal backups and easier to carry than a bulky device.
My first run with a card was pleasantly surprising. I tapped the card to my phone, approved a transaction, and it felt smooth—almost like contactless payment. At the same time, I noticed small annoyances, like the need for specific companion apps and occasional NFC quirks. Those are fixable, though, and they don’t undermine the core security model.
On one hand, smart cards simplify custody. On the other hand, they change failure modes. That matters. For instance, your typical seed-phrase problem—paper fire, theft, degradation—becomes a loss-and-recovery workflow problem instead. Do you print your recovery, split it, or store a metal backup somewhere safe? Think through that now because if you treat the card as a single point of failure, you’re asking for trouble. Split backups are very very important.
Hmm. Another point—multi-currency support varies. Some cards support many chains natively, others rely on third-party apps. Initially I assumed every wallet would handle all tokens, but the ecosystem is fragmented. This fragmentation can lead to UX gaps like delayed token support, and that bugs me. Still, the core capability—secure, on-card signing—remains the same across most reputable solutions.
On the mental model: people tend to anthropomorphize devices. They forget that a card is merely a secure locker with a rulebook. “It will never be hacked” is a dangerous thought. I try to remind myself and readers—threat models change, and hardware that looks simple can hide complexity under the hood. So a cautious mindset helps: treat the card as part of a system, not a magical talisman.
Here’s a quick, practical checklist I use when evaluating a smart-card wallet. First, check the secure element certification and firmware update policy. Second, test recovery procedures with small funds before moving large sums. Third, verify multi-currency compatibility for the chains you actually use. Fourth, factor in physical durability—will the card survive your life? Finally, consider how it fits with your daily habits. These may seem obvious, but people skip steps.
Whoa! A tiny anecdote—my friend kept his card in a back pocket and washed it with his jeans. It survived. Seriously, that durability sold him. But then he misplaced it for three days and panicked until his backup recovery was located. Lesson learned: durability is valuable, but backup discipline is non-negotiable.
Who should consider a smart-card wallet?
Short answer: pragmatic users who want strong security without a big learning curve. Medium answer: custodians who need many low-touch signers. Longer thought: if you travel a lot, dislike tiny screens, and need something unobtrusive for daily use, a card fits nicely because it slides into a wallet and acts like a key fob for your crypto life. It’s not the end-all for high-frequency traders or complex multi-sig setups, though some systems integrate cards into larger multisig schemes.
On balance, I recommend treating a smart card as a reliable primary signer combined with an air-gapped backup. That gives you the best of both worlds: everyday convenience and recoverability. I’m not 100% sure every reader will like the physicality, but many will appreciate the straightforward interaction model. (oh, and by the way… you can often pair it with mobile apps that mirror balances while keeping keys offline.)
Common questions about smart-card wallets
Are smart-card wallets secure against remote attacks?
Yes, generally. The private key stays in a secure element, so remote malware on your phone can’t extract it. However, attackers can still attempt social-engineering, man-in-the-middle bribes, or trick you into approving malicious transactions—so user caution is essential.
What happens if I lose the card?
You need a recovery procedure. Most vendors recommend generating a seed or recovery QR at setup and storing it securely (preferably a metal backup). Test recovery with small amounts before committing large balances.
Leave a Reply