Author: adminbackup

  • Polymarket for Election Night: Real-Time Probability Shifts and Live Trading Strategies

    Election night presents a unique opportunity for traders on Polymarket: results arrive sequentially, precinct-by-precinct, state-by-state, and the platform’s binary Yes/No share mechanism can shift dramatically as new vote counts surface. A race that appeared settled at 9 p.m. may tighten by 11 p.m. as mail ballots are processed, or a surprise lead in early reporting can evaporate once urban areas report their full counts. Polymarket’s architecture—using Polygon’s Layer-2 infrastructure, USDC settlement, and Automated Market Makers for continuous pricing—means these probability swings happen in real time, with prices reflecting aggregate trader belief within seconds of meaningful news.

    The operational reality differs sharply from traditional polling or cable-news commentary. Polymarket prices are not predictions about what commentators think will happen. They are direct expressions of where capital is willing to buy and sell, updated continuously as information arrives. A trader who understands which data sources move prices fastest, how Polymarket’s market structure responds to information asymmetries, and which positions to build or unwind during volatility can execute profitable trades within narrow windows. The question is not whether volatility exists during election nights. It is how to recognize signal from noise and act on it before the crowd does.

    Why election nights create Polymarket’s most volatile pricing

    Under normal conditions, Polymarket operates on known information: past election results, historical polling, demographic shifts, and long-term trend data. A contract trading 65% Yes means traders collectively assign a 65% probability to that outcome. But election night introduces a cascade of new, real information that was not available even hours earlier. A precinct report showing 55% support in a county that was expected to break 52-48 in the opposite direction creates immediate repricing pressure. The Automated Market Maker that powers Polymarket does not wait for consensus; it adjusts its prices mechanically as buy and sell orders flow in.

    The AMM mechanism itself amplifies volatility. When traders buy Yes shares rapidly, the AMM’s pricing algorithm increases the cost of further Yes purchases, creating a feedback loop that can drive prices up sharply. Conversely, if unexpected news arrives and traders rush to sell, the price drops steeply. On a traditional order-book exchange, large buy or sell orders might be absorbed by hidden liquidity or gradual accumulation. On Polymarket’s AMM-based system, significant order flow immediately moves the price. This design is efficient for avoiding manipulation and ensuring prices reflect current beliefs, but it also means big moves happen fast.

    Polymarket’s zero-fee trading via Polygon integration removes a friction that would normally exist. On centralized exchanges, a trader might hesitate to scalp a 2% move because trading fees would consume most of the profit. On Polymarket, a trader paying no fee can profit from smaller probability shifts, making even narrow windows tradeable. This fee structure also means that the largest traders—those moving millions of dollars of notional value—face no additional cost burden that might dampen their participation. The combination of AMM mechanics and zero fees creates conditions where information diffuses into prices almost instantly.

    The tamper-proof blockchain architecture also reinforces price-finding efficiency. Every transaction is immutable and timestamped. A trader cannot claim they executed at a better price than the chain shows. This auditability makes Polymarket an attractive venue for serious traders who want to justify their decision-making after the fact. It also means that price discovery is visible to everyone simultaneously, which can accelerate consensus-building once a major result appears.

    Information sources that move prices fastest on Polymarket

    Raw vote counts move Polymarket prices more than almost anything else. When the Associated Press or a state election office releases a batch of precinct results showing 100,000 new votes counted, traders immediately update their win probability assessments. A candidate trailing by 2% before the count who pulls even after it will see their Polymarket contract jump from 35% to 50% almost instantly. This is not because traders are rethinking anything; it is because the new fact—the actual vote—makes the old probability estimate wrong.

    Precinct-level granularity matters because it reveals which voter segments are breaking which way. A major city’s core precincts report earlier in some states and later in others. Experienced Polymarket traders know which precincts are bellwethers—historically representative of state outcomes—and which are outliers. A precinct that usually breaks 70-30 for one party but appears on track for 65-35 might signal a shift in that demographic. The Polymarket price can move not because the final result is predetermined, but because traders are updating their probability estimates based on how actual voter behavior is tracking relative to historical patterns.

    Cable news calls are a different beast. When a major network decides to call a state for one candidate, Polymarket often reacts with a sharp move, but the move is less about new information and more about coordination. Everyone watching television sees the same call simultaneously. Traders who have been trying to hedge or position ahead of that call now see it confirmed, and they adjust. This is important: Polymarket prices may move sharply on a call, but the call itself usually reflects data that professional data analysts already had. The real money is often made before the call, by traders who act on the raw precinct data that the calls are based on.

    Unexpected precinct results sometimes move Polymarket faster than news coverage. A precinct that was supposed to report at 10 p.m. but reports at 9:45 p.m., showing an unexpected result, will move prices immediately among traders monitoring the raw data feeds. Cable news may not mention that precinct for another 15 minutes. By then, the Polymarket price has already adjusted and the profit opportunity has closed. This time lag between raw data and media coverage has narrowed significantly in recent election cycles as traders have gotten faster at ingesting and processing precinct-level results, but it still exists.

    Margin and liquidity constraints can also create price movements on Polymarket that are technically temporary. If a major bet goes through, a trader might need to immediately hedge by buying the opposite side. This can create a price move that does not reflect changing beliefs about the outcome but rather reflects a forced rebalance. Traders aware of large positions sometimes try to squeeze these moves by accumulating shares ahead of expected hedging. These cat-and-mouse dynamics are less pronounced on Polymarket than on leverage-heavy trading venues, but they still occur.

    Building positions before election night and managing them during

    Many serious traders on Polymarket do not wait until election night to build their core positions. They accumulate shares days or weeks in advance, sizing positions based on their conviction and their risk tolerance. The advantage of this approach is that you can average your cost across multiple price points, and you can avoid being part of the election-night panic that can move prices irrationally. The disadvantage is that you have capital tied up during the waiting period, and you are exposed to any news that might shift beliefs before a single vote is counted.

    On election night itself, the question becomes how to adjust existing positions. A trader who bought Yes shares at 60% because they believed the true probability was 70% faces a different problem once results start arriving. If the first wave of precinct data shows the candidate performing worse than expected and the price drops to 50%, the trader must decide whether to average down (buying more at a worse price, betting on a reversal) or to cut the position and preserve capital. The decision depends partly on whether the precinct results are actually negative or just represent a particular group that votes early and skews in a certain direction.

    Hedging becomes more active on election night. A trader who entered with a large Yes position might buy No shares if the price drops sharply, accepting a loss on the Yes side to cap further downside. This is typically more expensive later in the night because volatility moves both directions, but the downside protection is valuable when you do not know what the next precinct report will show. Polymarket’s low fees make this dynamic hedging feasible in a way it would not be on platforms with trading costs.

    Scalping—buying and selling rapidly to capture small moves—is also more active during election nights. A trader who sees the Yes price move from 55% to 57% might buy, hold for 30 seconds until the price moves to 58%, and sell. On a traditional exchange, this would be expensive and potentially dangerous if liquidity dries up. On Polymarket, with zero fees and an AMM that is always available to take the other side, this can be a viable tactic. The key is recognizing that scalp trades are real profits (or losses) captured from the AMM, not from other traders. The AMM’s price curve gradually reflects the aggregate direction of all that buying and selling.

    Recognizing false signals and avoiding whipsaw trades

    Early-night volatility on Polymarket can be especially misleading because precinct reporting patterns are geographically uneven. In many states, rural precincts report earlier and urban precincts report later. Rural voters typically skew toward one party, while urban voters skew toward the other. A trader watching Polymarket in the first two hours of the night might see the underdog’s contract price soar because rural precincts that favor them are reporting first. The price might reach 70%, suggesting a strong position, even though the state ultimately breaks the other way once cities are counted.

    This is why experienced Polymarket traders obsess over which precincts are expected to report when. They cross-reference state election office estimates, historical patterns, and news reports about outstanding ballots. A 10-point jump in one candidate’s share on Polymarket might be real, or it might just be an artifact of which geography has been counted so far. The traders who make money are usually those who recognize that the move is predictable and temporary, and who position accordingly. If you know that urban areas have 40% of the vote and report after 11 p.m., and those areas favor one candidate by 20 points, you can estimate how much the Polymarket price is likely to shift once they are counted, and you can position ahead of that shift.

    Unexpected turnout also creates false signals. If a precinct sees 20% higher turnout than in the previous election, that can shift how you interpret the candidate’s performance in that precinct. Higher turnout often favors Democrats in the United States, but not always and not uniformly. Traders who misinterpret a turnout surprise can get caught scaling in or out at the wrong time. The safest approach is to wait for a meaningful volume of results before acting aggressively. A single precinct reporting unusually is noise. Five precincts from different regions reporting in the same direction is signal.

    Stop-losses and profit-taking become particularly important on election nights because volatility can overshoot. A trader who set a limit order to sell Yes shares if the price hit 75% should expect that order to execute if it does reach that level, sometimes just minutes after a dramatic move. This prevents you from being caught holding the bag when a subsequent precinct report reverses the move. The downside of stop-losses is that they can lock in losses just before a reversal, but on election nights with sequential information arrival, the benefits usually outweigh the costs.

    Why institutional traders and arbitrage desks focus on Polymarket during elections

    Polymarket attracts institutional traders during major elections because the prices are genuinely uncertain and there is real money at stake. A hedge fund with exposure to election outcomes—perhaps through equity or currency positions—can use Polymarket to hedge that exposure. A macro fund betting on policy changes might size that bet partly through polymarket contracts, which provide transparent pricing and no custody risk beyond the smart contract. The platform’s tamper-proof blockchain architecture and UMA oracle dispute resolution also make it credible to professional traders who need assurance that they will be able to exit their positions and receive settled funds.

    Arbitrage desks also profit from Polymarket pricing inefficiencies relative to traditional betting markets and polling aggregators. If Polymarket prices one candidate at 45% and a traditional prediction market or betting exchange prices the same candidate at 48%, an arbitrageur can buy on Polymarket and sell on the other platform, locking in a profit. These arbitrage windows close quickly, but they open repeatedly during elections because information reaches different platforms at different speeds and different participant bases believe different things. Election nights create the widest and most frequent arbitrage opportunities because prices are most volatile and participants are most concentrated on real-time data.

    Polymarket’s zero-fee structure makes small arbitrage margins economical at scale. A 1% difference between two platforms might not justify execution costs on a traditional exchange, but on Polymarket, with no trading fee, it becomes profitable. This creates a flattening effect where Polymarket prices tend to align with other platforms faster than they otherwise would. The traders executing these arbitrages are not making directional bets. They are just harvesting pricing differences, and their activity makes Polymarket more efficient and less profitable for pure directional traders.

    Regulatory and technical risks during high-volume nights

    Polymarket’s Layer-2 Polygon infrastructure generally handles election-night volume smoothly, but extreme congestion is possible. If millions of dollars of bets are flowing through simultaneously, transaction costs on Polygon could spike and confirmation times could lengthen. This is unlikely on Polygon specifically because it is designed for high throughput, but it is not impossible. A trader trying to exit a position as results turn bad might find that their transaction is stuck in a mempool and cannot execute at the price they expected.

    UMA oracle disputes also introduce a small tail risk. Most Polymarket contracts settle unambiguously—a candidate either wins or loses—but disputes can arise if the outcome is very close or if a state’s official results are contested. The UMA oracle resolution process can take time, and during that time, traders cannot be certain of the final settlement price. In extreme cases, a disputed election could lead to UMA token-holder voting on how a contract settles, introducing political economy into the resolution process. This is a known limitation of Polymarket’s design and is acceptable to most users, but it is a real risk that should be acknowledged.

    Regulatory scrutiny of Polymarket varies by jurisdiction. In some countries, prediction markets are treated as unlicensed betting and face restrictions. In the United States, Polymarket operates in a legal gray area that has so far tolerated its existence but could change. A trader placing large bets on Polymarket should understand that their jurisdiction might classify the platform differently than others do, and that regulatory changes could affect their ability to trade or withdraw funds. The decentralized and censorship-resistant aspects of Polymarket are designed to reduce this risk, but they do not eliminate it entirely.

    Political prediction markets and the wisdom of crowds

    The underlying principle behind Polymarket is the wisdom of crowds—the idea that aggregate beliefs of many decentralized participants usually converge on accurate probabilities faster than any individual expert. Election-night results test this principle directly. Polymarket prices at any given moment reflect the aggregate belief of all traders with money at stake. If that aggregate belief diverges from actual results, traders lose money and the market is shown to have been wrong. But the mechanism that ensures Polymarket prices are grounded in reality is the same mechanism that makes them profitable to trade against: real outcomes that contradict the market’s pricing create opportunities for traders who saw something the crowd missed.

    During elections, this plays out in real time. If Polymarket prices a candidate at 55% but they actually end up at 60% after all votes are counted, it means the traders who bet on that candidate at higher conviction outperformed the broader market. Conversely, if the market prices a candidate at 55% and they end up losing with 48%, it means the market was overconfident. The election night itself provides immediate feedback on whether the crowd’s aggregate belief was accurate. This feedback loop—and the profit incentive that drives it—keeps Polymarket prices tethered to reality in ways that pure speculation or casual betting might not be.

    The practical implication for traders is that Polymarket prices should be treated as genuine probability estimates, not entertainment or indicators of who should win. A candidate priced at 30% is not a longshot play on an unlikely hero. They are a candidate for whom the trading community, on aggregate, sees three chances in ten. The distinction matters because it affects how you should size positions and what you should expect in terms of volatility and final outcomes.

    Execution tactics for the night itself

    Traders who plan to be active on Polymarket during an election should prepare the night before. This means having funds deposited, positions sized, research completed, and contingencies planned. You should know which precincts matter, when major vote dumps are expected, and what precinct results would surprise you. You should also know your exit plans: at what price will you close winning positions, at what loss will you cut losers, and what changes in information would cause you to abandon your thesis entirely.

    During the night, monitoring becomes critical. Real-time precinct data is available from AP, state election offices, and aggregator sites like FiveThirtyEight’s election tracker. Comparing Polymarket prices to this data lets you spot dislocations. If a precinct reports and moves a state’s margin by 0.5 points, you can estimate roughly how much that should move the Polymarket price for that state, and you can check whether the market has caught up yet. If it has not, there is an opportunity. If it has over-adjusted, there is a different opportunity on the other side.

    Position management during the night is active. This is not a set-and-forget exercise. You should be willing to take profits on out-of-the-money positions, cut losses when your thesis changes, and add to positions that are performing better than expected but that you still have conviction in. The key is to remain disciplined: avoid the temptation to chase moves just because they look exciting, and avoid holding positions purely out of stubbornness. The market is right more often than you are, even if you are skilled.

    Margin and leverage should be avoided or used with extreme caution. Polymarket does not offer margin directly, but if you have used leverage elsewhere to fund positions, you are vulnerable to a margin call if positions move against you sharply. Election-night volatility is precisely when leverage tends to blow up accounts. Unless you have a specific reason to use leverage and have sized it conservatively, it is not worth the risk.

    Frequently asked questions

    How quickly do Polymarket prices update during election night?

    Polymarket prices update in real time as traders buy and sell, typically within seconds of new information or large order flows. Because the platform runs on Polygon Layer-2 and uses Automated Market Makers, prices adjust mechanically and continuously rather than waiting for a dealer or exchange to match orders. Zero trading fees mean traders can respond to small price movements profitably, which further accelerates price discovery.

    Which precinct results move Polymarket prices the most?

    Large, historically representative precincts or those with unexpected results move prices sharply. A precinct that usually breaks 65-35 but appears on track for 58-42 signals a meaningful demographic or turnout shift. Early-reporting precincts that are atypical of a state’s composition can create temporary Polymarket price moves that are later reversed once more representative areas are counted. Traders who understand the state’s precinct composition can predict these moves ahead of time.

    Can you profit from political prediction markets without taking directional bets?

    Yes, arbitrage desks exploit pricing differences between Polymarket and other platforms, and scalpers capture small moves within the Automated Market Maker’s curve. These traders are not betting on outcomes; they are capturing market inefficiencies. However, arbitrage margins are usually small and close quickly, requiring speed and low-cost access. Most retail traders on Polymarket are making directional probability bets, not executing arbitrage.

  • Polymarket for Election Night: Real-Time Probability Shifts and Live Trading Strategies

    Election night presents a unique opportunity for traders on Polymarket: results arrive sequentially, precinct-by-precinct, state-by-state, and the platform’s binary Yes/No share mechanism can shift dramatically as new vote counts surface. A race that appeared settled at 9 p.m. may tighten by 11 p.m. as mail ballots are processed, or a surprise lead in early reporting can evaporate once urban areas report their full counts. Polymarket’s architecture—using Polygon’s Layer-2 infrastructure, USDC settlement, and Automated Market Makers for continuous pricing—means these probability swings happen in real time, with prices reflecting aggregate trader belief within seconds of meaningful news.

    The operational reality differs sharply from traditional polling or cable-news commentary. Polymarket prices are not predictions about what commentators think will happen. They are direct expressions of where capital is willing to buy and sell, updated continuously as information arrives. A trader who understands which data sources move prices fastest, how Polymarket’s market structure responds to information asymmetries, and which positions to build or unwind during volatility can execute profitable trades within narrow windows. The question is not whether volatility exists during election nights. It is how to recognize signal from noise and act on it before the crowd does.

    Why election nights create Polymarket’s most volatile pricing

    Under normal conditions, Polymarket operates on known information: past election results, historical polling, demographic shifts, and long-term trend data. A contract trading 65% Yes means traders collectively assign a 65% probability to that outcome. But election night introduces a cascade of new, real information that was not available even hours earlier. A precinct report showing 55% support in a county that was expected to break 52-48 in the opposite direction creates immediate repricing pressure. The Automated Market Maker that powers Polymarket does not wait for consensus; it adjusts its prices mechanically as buy and sell orders flow in.

    The AMM mechanism itself amplifies volatility. When traders buy Yes shares rapidly, the AMM’s pricing algorithm increases the cost of further Yes purchases, creating a feedback loop that can drive prices up sharply. Conversely, if unexpected news arrives and traders rush to sell, the price drops steeply. On a traditional order-book exchange, large buy or sell orders might be absorbed by hidden liquidity or gradual accumulation. On Polymarket’s AMM-based system, significant order flow immediately moves the price. This design is efficient for avoiding manipulation and ensuring prices reflect current beliefs, but it also means big moves happen fast.

    Polymarket’s zero-fee trading via Polygon integration removes a friction that would normally exist. On centralized exchanges, a trader might hesitate to scalp a 2% move because trading fees would consume most of the profit. On Polymarket, a trader paying no fee can profit from smaller probability shifts, making even narrow windows tradeable. This fee structure also means that the largest traders—those moving millions of dollars of notional value—face no additional cost burden that might dampen their participation. The combination of AMM mechanics and zero fees creates conditions where information diffuses into prices almost instantly.

    The tamper-proof blockchain architecture also reinforces price-finding efficiency. Every transaction is immutable and timestamped. A trader cannot claim they executed at a better price than the chain shows. This auditability makes Polymarket an attractive venue for serious traders who want to justify their decision-making after the fact. It also means that price discovery is visible to everyone simultaneously, which can accelerate consensus-building once a major result appears.

    Information sources that move prices fastest on Polymarket

    Raw vote counts move Polymarket prices more than almost anything else. When the Associated Press or a state election office releases a batch of precinct results showing 100,000 new votes counted, traders immediately update their win probability assessments. A candidate trailing by 2% before the count who pulls even after it will see their Polymarket contract jump from 35% to 50% almost instantly. This is not because traders are rethinking anything; it is because the new fact—the actual vote—makes the old probability estimate wrong.

    Precinct-level granularity matters because it reveals which voter segments are breaking which way. A major city’s core precincts report earlier in some states and later in others. Experienced Polymarket traders know which precincts are bellwethers—historically representative of state outcomes—and which are outliers. A precinct that usually breaks 70-30 for one party but appears on track for 65-35 might signal a shift in that demographic. The Polymarket price can move not because the final result is predetermined, but because traders are updating their probability estimates based on how actual voter behavior is tracking relative to historical patterns.

    Cable news calls are a different beast. When a major network decides to call a state for one candidate, Polymarket often reacts with a sharp move, but the move is less about new information and more about coordination. Everyone watching television sees the same call simultaneously. Traders who have been trying to hedge or position ahead of that call now see it confirmed, and they adjust. This is important: Polymarket prices may move sharply on a call, but the call itself usually reflects data that professional data analysts already had. The real money is often made before the call, by traders who act on the raw precinct data that the calls are based on.

    Unexpected precinct results sometimes move Polymarket faster than news coverage. A precinct that was supposed to report at 10 p.m. but reports at 9:45 p.m., showing an unexpected result, will move prices immediately among traders monitoring the raw data feeds. Cable news may not mention that precinct for another 15 minutes. By then, the Polymarket price has already adjusted and the profit opportunity has closed. This time lag between raw data and media coverage has narrowed significantly in recent election cycles as traders have gotten faster at ingesting and processing precinct-level results, but it still exists.

    Margin and liquidity constraints can also create price movements on Polymarket that are technically temporary. If a major bet goes through, a trader might need to immediately hedge by buying the opposite side. This can create a price move that does not reflect changing beliefs about the outcome but rather reflects a forced rebalance. Traders aware of large positions sometimes try to squeeze these moves by accumulating shares ahead of expected hedging. These cat-and-mouse dynamics are less pronounced on Polymarket than on leverage-heavy trading venues, but they still occur.

    Building positions before election night and managing them during

    Many serious traders on Polymarket do not wait until election night to build their core positions. They accumulate shares days or weeks in advance, sizing positions based on their conviction and their risk tolerance. The advantage of this approach is that you can average your cost across multiple price points, and you can avoid being part of the election-night panic that can move prices irrationally. The disadvantage is that you have capital tied up during the waiting period, and you are exposed to any news that might shift beliefs before a single vote is counted.

    On election night itself, the question becomes how to adjust existing positions. A trader who bought Yes shares at 60% because they believed the true probability was 70% faces a different problem once results start arriving. If the first wave of precinct data shows the candidate performing worse than expected and the price drops to 50%, the trader must decide whether to average down (buying more at a worse price, betting on a reversal) or to cut the position and preserve capital. The decision depends partly on whether the precinct results are actually negative or just represent a particular group that votes early and skews in a certain direction.

    Hedging becomes more active on election night. A trader who entered with a large Yes position might buy No shares if the price drops sharply, accepting a loss on the Yes side to cap further downside. This is typically more expensive later in the night because volatility moves both directions, but the downside protection is valuable when you do not know what the next precinct report will show. Polymarket’s low fees make this dynamic hedging feasible in a way it would not be on platforms with trading costs.

    Scalping—buying and selling rapidly to capture small moves—is also more active during election nights. A trader who sees the Yes price move from 55% to 57% might buy, hold for 30 seconds until the price moves to 58%, and sell. On a traditional exchange, this would be expensive and potentially dangerous if liquidity dries up. On Polymarket, with zero fees and an AMM that is always available to take the other side, this can be a viable tactic. The key is recognizing that scalp trades are real profits (or losses) captured from the AMM, not from other traders. The AMM’s price curve gradually reflects the aggregate direction of all that buying and selling.

    Recognizing false signals and avoiding whipsaw trades

    Early-night volatility on Polymarket can be especially misleading because precinct reporting patterns are geographically uneven. In many states, rural precincts report earlier and urban precincts report later. Rural voters typically skew toward one party, while urban voters skew toward the other. A trader watching Polymarket in the first two hours of the night might see the underdog’s contract price soar because rural precincts that favor them are reporting first. The price might reach 70%, suggesting a strong position, even though the state ultimately breaks the other way once cities are counted.

    This is why experienced Polymarket traders obsess over which precincts are expected to report when. They cross-reference state election office estimates, historical patterns, and news reports about outstanding ballots. A 10-point jump in one candidate’s share on Polymarket might be real, or it might just be an artifact of which geography has been counted so far. The traders who make money are usually those who recognize that the move is predictable and temporary, and who position accordingly. If you know that urban areas have 40% of the vote and report after 11 p.m., and those areas favor one candidate by 20 points, you can estimate how much the Polymarket price is likely to shift once they are counted, and you can position ahead of that shift.

    Unexpected turnout also creates false signals. If a precinct sees 20% higher turnout than in the previous election, that can shift how you interpret the candidate’s performance in that precinct. Higher turnout often favors Democrats in the United States, but not always and not uniformly. Traders who misinterpret a turnout surprise can get caught scaling in or out at the wrong time. The safest approach is to wait for a meaningful volume of results before acting aggressively. A single precinct reporting unusually is noise. Five precincts from different regions reporting in the same direction is signal.

    Stop-losses and profit-taking become particularly important on election nights because volatility can overshoot. A trader who set a limit order to sell Yes shares if the price hit 75% should expect that order to execute if it does reach that level, sometimes just minutes after a dramatic move. This prevents you from being caught holding the bag when a subsequent precinct report reverses the move. The downside of stop-losses is that they can lock in losses just before a reversal, but on election nights with sequential information arrival, the benefits usually outweigh the costs.

    Why institutional traders and arbitrage desks focus on Polymarket during elections

    Polymarket attracts institutional traders during major elections because the prices are genuinely uncertain and there is real money at stake. A hedge fund with exposure to election outcomes—perhaps through equity or currency positions—can use Polymarket to hedge that exposure. A macro fund betting on policy changes might size that bet partly through polymarket contracts, which provide transparent pricing and no custody risk beyond the smart contract. The platform’s tamper-proof blockchain architecture and UMA oracle dispute resolution also make it credible to professional traders who need assurance that they will be able to exit their positions and receive settled funds.

    Arbitrage desks also profit from Polymarket pricing inefficiencies relative to traditional betting markets and polling aggregators. If Polymarket prices one candidate at 45% and a traditional prediction market or betting exchange prices the same candidate at 48%, an arbitrageur can buy on Polymarket and sell on the other platform, locking in a profit. These arbitrage windows close quickly, but they open repeatedly during elections because information reaches different platforms at different speeds and different participant bases believe different things. Election nights create the widest and most frequent arbitrage opportunities because prices are most volatile and participants are most concentrated on real-time data.

    Polymarket’s zero-fee structure makes small arbitrage margins economical at scale. A 1% difference between two platforms might not justify execution costs on a traditional exchange, but on Polymarket, with no trading fee, it becomes profitable. This creates a flattening effect where Polymarket prices tend to align with other platforms faster than they otherwise would. The traders executing these arbitrages are not making directional bets. They are just harvesting pricing differences, and their activity makes Polymarket more efficient and less profitable for pure directional traders.

    Regulatory and technical risks during high-volume nights

    Polymarket’s Layer-2 Polygon infrastructure generally handles election-night volume smoothly, but extreme congestion is possible. If millions of dollars of bets are flowing through simultaneously, transaction costs on Polygon could spike and confirmation times could lengthen. This is unlikely on Polygon specifically because it is designed for high throughput, but it is not impossible. A trader trying to exit a position as results turn bad might find that their transaction is stuck in a mempool and cannot execute at the price they expected.

    UMA oracle disputes also introduce a small tail risk. Most Polymarket contracts settle unambiguously—a candidate either wins or loses—but disputes can arise if the outcome is very close or if a state’s official results are contested. The UMA oracle resolution process can take time, and during that time, traders cannot be certain of the final settlement price. In extreme cases, a disputed election could lead to UMA token-holder voting on how a contract settles, introducing political economy into the resolution process. This is a known limitation of Polymarket’s design and is acceptable to most users, but it is a real risk that should be acknowledged.

    Regulatory scrutiny of Polymarket varies by jurisdiction. In some countries, prediction markets are treated as unlicensed betting and face restrictions. In the United States, Polymarket operates in a legal gray area that has so far tolerated its existence but could change. A trader placing large bets on Polymarket should understand that their jurisdiction might classify the platform differently than others do, and that regulatory changes could affect their ability to trade or withdraw funds. The decentralized and censorship-resistant aspects of Polymarket are designed to reduce this risk, but they do not eliminate it entirely.

    Political prediction markets and the wisdom of crowds

    The underlying principle behind Polymarket is the wisdom of crowds—the idea that aggregate beliefs of many decentralized participants usually converge on accurate probabilities faster than any individual expert. Election-night results test this principle directly. Polymarket prices at any given moment reflect the aggregate belief of all traders with money at stake. If that aggregate belief diverges from actual results, traders lose money and the market is shown to have been wrong. But the mechanism that ensures Polymarket prices are grounded in reality is the same mechanism that makes them profitable to trade against: real outcomes that contradict the market’s pricing create opportunities for traders who saw something the crowd missed.

    During elections, this plays out in real time. If Polymarket prices a candidate at 55% but they actually end up at 60% after all votes are counted, it means the traders who bet on that candidate at higher conviction outperformed the broader market. Conversely, if the market prices a candidate at 55% and they end up losing with 48%, it means the market was overconfident. The election night itself provides immediate feedback on whether the crowd’s aggregate belief was accurate. This feedback loop—and the profit incentive that drives it—keeps Polymarket prices tethered to reality in ways that pure speculation or casual betting might not be.

    The practical implication for traders is that Polymarket prices should be treated as genuine probability estimates, not entertainment or indicators of who should win. A candidate priced at 30% is not a longshot play on an unlikely hero. They are a candidate for whom the trading community, on aggregate, sees three chances in ten. The distinction matters because it affects how you should size positions and what you should expect in terms of volatility and final outcomes.

    Execution tactics for the night itself

    Traders who plan to be active on Polymarket during an election should prepare the night before. This means having funds deposited, positions sized, research completed, and contingencies planned. You should know which precincts matter, when major vote dumps are expected, and what precinct results would surprise you. You should also know your exit plans: at what price will you close winning positions, at what loss will you cut losers, and what changes in information would cause you to abandon your thesis entirely.

    During the night, monitoring becomes critical. Real-time precinct data is available from AP, state election offices, and aggregator sites like FiveThirtyEight’s election tracker. Comparing Polymarket prices to this data lets you spot dislocations. If a precinct reports and moves a state’s margin by 0.5 points, you can estimate roughly how much that should move the Polymarket price for that state, and you can check whether the market has caught up yet. If it has not, there is an opportunity. If it has over-adjusted, there is a different opportunity on the other side.

    Position management during the night is active. This is not a set-and-forget exercise. You should be willing to take profits on out-of-the-money positions, cut losses when your thesis changes, and add to positions that are performing better than expected but that you still have conviction in. The key is to remain disciplined: avoid the temptation to chase moves just because they look exciting, and avoid holding positions purely out of stubbornness. The market is right more often than you are, even if you are skilled.

    Margin and leverage should be avoided or used with extreme caution. Polymarket does not offer margin directly, but if you have used leverage elsewhere to fund positions, you are vulnerable to a margin call if positions move against you sharply. Election-night volatility is precisely when leverage tends to blow up accounts. Unless you have a specific reason to use leverage and have sized it conservatively, it is not worth the risk.

    Frequently asked questions

    How quickly do Polymarket prices update during election night?

    Polymarket prices update in real time as traders buy and sell, typically within seconds of new information or large order flows. Because the platform runs on Polygon Layer-2 and uses Automated Market Makers, prices adjust mechanically and continuously rather than waiting for a dealer or exchange to match orders. Zero trading fees mean traders can respond to small price movements profitably, which further accelerates price discovery.

    Which precinct results move Polymarket prices the most?

    Large, historically representative precincts or those with unexpected results move prices sharply. A precinct that usually breaks 65-35 but appears on track for 58-42 signals a meaningful demographic or turnout shift. Early-reporting precincts that are atypical of a state’s composition can create temporary Polymarket price moves that are later reversed once more representative areas are counted. Traders who understand the state’s precinct composition can predict these moves ahead of time.

    Can you profit from political prediction markets without taking directional bets?

    Yes, arbitrage desks exploit pricing differences between Polymarket and other platforms, and scalpers capture small moves within the Automated Market Maker’s curve. These traders are not betting on outcomes; they are capturing market inefficiencies. However, arbitrage margins are usually small and close quickly, requiring speed and low-cost access. Most retail traders on Polymarket are making directional probability bets, not executing arbitrage.

  • Is a Tangem Card Really Cold Storage—or Just a Simpler Hardware Wallet?

    What if the most important feature of a hardware wallet is not its screen, metal casing, or number of supported assets, but the moment when its private key is created? That question cuts through much of the marketing language around card-based crypto storage. A Tangem card is designed to keep key operations inside a secure hardware element while using near-field communication (NFC) to interact with a phone. The result is compact, convenient, and deliberately different from the familiar USB-style wallet.

    That difference matters for US users deciding how to protect Bitcoin, Ethereum, and other digital assets. A card can reduce friction, but it does not eliminate operational risk. It may be easier to carry than a traditional device, yet recovery, backup design, phone security, transaction verification, and supply-chain trust still shape the real security outcome. The right mental model is not “a bank card for crypto.” It is a small signing device whose interface has been moved to a smartphone.

    The first myth: cold storage means the wallet never connects

    Cold storage is commonly described as keeping crypto offline. Strictly speaking, the assets themselves remain on a blockchain; what stays protected is the private key used to authorize transactions. A hardware wallet attempts to keep that key away from an internet-connected environment, even when the wallet communicates with an application.

    An NFC card can therefore operate as cold storage while still being tapped against a phone. NFC is a short-range communication method, not the same thing as giving the phone unrestricted access to the private key. In a properly designed system, the card performs or authorizes cryptographic operations internally, while the phone prepares transaction data and broadcasts the signed result. The phone may be online; the key should not be exported to it.

    This separation is the central mechanism. The blockchain does not know whether a transaction was signed by a card, a USB device, or software running on a laptop. It only verifies the resulting digital signature. Security depends on whether the secret needed to produce that signature remains protected and whether the user can accurately confirm what is being signed.

    That last point is often overlooked. Hardware isolation protects against some forms of key theft, but it cannot automatically protect a user who approves the wrong recipient address, a malicious token allowance, or an unexpected decentralized-application request. A secure signer can faithfully authorize a bad transaction. Cold storage reduces one category of risk; it does not replace judgment.

    What makes a card-based hardware wallet attractive

    The strongest argument for a Tangem card is behavioral rather than cosmetic. Traditional hardware wallets can be highly capable, but they introduce a device to charge, store, update, and physically connect. A card can fit into an everyday routine with less friction. Tapping a card to a phone is intuitive, especially for users who already rely on mobile banking and contactless payments.

    Less friction can improve security when it prevents users from leaving funds on an exchange or moving private keys into a general-purpose phone wallet simply because the safer alternative feels complicated. This is a practical lesson from security engineering: a control that people consistently use may be more valuable than a theoretically stronger control that they routinely bypass.

    The card format also changes the threat surface. There is no need for a cable connection during ordinary use, and the private key is intended to remain in the card’s secure hardware. But convenience introduces dependencies. The user needs a compatible phone, a trustworthy wallet application, a functioning card, and a recovery plan. If the card is lost, damaged, or unavailable, access depends on how backup cards or other recovery arrangements were configured.

    Recent project messaging positions Tangem as a simple cold Bitcoin wallet for buying, selling, and storing Bitcoin, Ethereum, and other crypto assets. That emphasis on simplicity is meaningful for newcomers, but it should be read as an interface claim rather than a promise that crypto custody has become risk-free. Simplicity moves complexity out of the visible interface; it does not make the underlying responsibility disappear.

    The second myth: multiple cards automatically mean a complete backup

    Card-based systems often appeal because users can hold more than one physical card. That can be useful, but a second card is not automatically equivalent to a traditional written recovery phrase. The security properties depend on how the wallet creates, distributes, and restores the key material, as well as on the user’s setup choices.

    A recovery phrase is a human-readable secret that can often be restored across compatible wallets. A card-based backup arrangement may instead rely on additional cards or another defined recovery method. These are different trust models. A phrase is portable but dangerous if photographed, copied to cloud storage, or exposed to malware. Physical backup cards can reduce typing and transcription errors, but they introduce questions about how many copies exist, where they are stored, and whether one person can access enough of them to authorize funds.

    The useful framework is to separate three questions: Can the wallet sign a transaction? Can the owner recover access after loss? Can an attacker obtain enough information or physical access to do either? A setup that answers only the first question is incomplete. For substantial holdings, users should consider geographically separate storage, controlled access, and a written record of the recovery procedure that does not reveal more secret information than necessary.

    There is also a boundary condition around inheritance and emergencies. A recovery plan that makes sense to its creator may be opaque to a family member or executor. A robust plan should explain the existence of the assets, the location of relevant cards or instructions, and the sequence for recovery—without placing sensitive secrets in an easily copied digital file. This is less glamorous than choosing a wallet, but it is where long-term custody plans often fail.

    Where the smartphone helps—and where it becomes a liability

    The phone is the card wallet’s interface, not necessarily its vault. It displays balances, helps construct transactions, and may connect to exchanges or decentralized applications. That makes the experience accessible, but it also means users must distinguish between the phone’s view and the card’s authority.

    A compromised phone could potentially misrepresent a recipient address or transaction amount. The exact protections available depend on the wallet’s design and what the card can display or verify. Users should treat high-value transactions differently from routine transfers: check the destination, network, asset, and amount; avoid approving unexpected prompts; and be cautious with links, browser extensions, and support messages that request recovery information.

    NFC itself should not be treated as a magic security shield. Short range can reduce casual interception opportunities, but proximity is not the same as authentication. The meaningful question is whether the card’s cryptographic design prevents private-key extraction and whether transaction authorization requires the right physical and software conditions. NFC provides the communication channel; secure key handling provides the core security property.

    For readers comparing options, a useful starting point is the tangem wallet overview, followed by independent verification of supported assets, recovery behavior, fees, application permissions, and update practices. Product documentation is most valuable when it answers operational questions, not merely when it lists security adjectives.

    A decision framework for US users

    There is no universally best hardware wallet. The better choice depends on the user’s threat model—the realistic ways funds might be lost or stolen. Someone making frequent small transactions may prioritize convenience and quick access. Someone holding long-term savings may prioritize recoverability, transaction verification, multisignature arrangements, and separation from daily devices.

    Consider four dimensions. First is key isolation: does the private key remain inside dedicated hardware, and under what conditions can it be used? Second is recovery: what happens if every card is lost, the phone is replaced, or the application changes? Third is verification: can the user confidently inspect what the device is authorizing? Fourth is operational fit: will the owner actually store backups safely and follow the process consistently?

    For US users, tax and reporting responsibilities add another practical layer. A wallet does not calculate the legal consequences of buying, selling, swapping, or transferring assets. Users should preserve transaction records and understand that self-custody changes control of keys, not the underlying reporting obligations. Convenience at the custody layer should not be confused with administrative simplicity.

    Card-based hardware wallets are especially compelling when the main problem is unsafe convenience: leaving funds on an exchange, reusing weak passwords, or importing a private key into an untrusted application. They are less obviously sufficient when the main problem is complex approval workflows, institutional custody, or the need for transparent, independently verifiable recovery across many operators.

    What to watch as card wallets mature

    The next important developments are unlikely to be judged only by whether a wallet is thinner or faster. Watch how clearly products explain key generation, backup assumptions, firmware or application updates, transaction confirmation, and support boundaries. Security improves when users can understand the system’s trust assumptions without needing to infer them from marketing language.

    A plausible forward-looking scenario is that NFC wallets expand adoption among people who find conventional hardware wallets intimidating. That outcome would be beneficial if simpler onboarding moves users toward self-custody without hiding recovery responsibilities. The limiting factor will be education: a tap-based experience may reduce technical friction, but it can also encourage users to approve transactions without understanding the authorization being made.

    The sharper conclusion is that cold storage is a process, not a product category. A Tangem card can provide strong key-isolation benefits and a practical interface, but its security depends on setup, backup, phone hygiene, transaction discipline, and the user’s recovery plan. Choose the card if its model matches those responsibilities—not because the form factor makes them vanish.

    Frequently asked questions

    Is a Tangem card the same as keeping cryptocurrency offline?

    It can serve as a cold-storage device when private keys remain protected inside the card and the phone is used mainly as an interface. The phone may connect to the internet, but the key should not be exported. The security result depends on the wallet’s implementation and the user’s transaction practices.

    What is the biggest risk of using an NFC hardware wallet?

    The biggest risk is often not NFC interception but user error: approving a malicious transaction, mishandling backups, exposing recovery information, or trusting a fake support channel. NFC reduces some connection friction, yet it does not verify that every transaction is legitimate.

    Should a card wallet replace an exchange for long-term storage?

    For users who understand self-custody and maintain a recovery plan, a hardware wallet can reduce dependence on an exchange’s account and withdrawal systems. It also transfers responsibility to the user. The decision should account for backup, inheritance, transaction frequency, and the value of assets being protected.

  • Trezor Wallet in Practice: What Its Security Model Really Protects

    You are moving a meaningful amount of cryptocurrency from an exchange to a new wallet. The address appears correct on your laptop, the network fee looks reasonable, and then a small screen on the Trezor device asks you to confirm the recipient. That extra step can feel inconvenient, but it is the central idea behind a hardware wallet: the computer prepares a transaction, while the device provides the trusted point at which authorization occurs.

    Trezor is therefore more than a USB gadget for storing coins. It is a system combining offline private-key storage, a physical approval boundary, recovery procedures, and companion software. Its advantages are substantial, but they are not magical. A Trezor can reduce exposure to malware and phishing; it cannot correct a user who approves a fraudulent transaction, loses a recovery phrase, or installs an imitation application.

    How the Trezor security model works

    In a conventional online wallet, private keys are exposed to an internet-connected operating environment, even if protected by passwords or encryption. Trezor changes that arrangement by generating and retaining private keys on the device. The keys do not leave the hardware during normal operation. A computer can request that a transaction be signed, but the signing operation occurs on the Trezor itself.

    The distinction matters because many cryptocurrency attacks are not attempts to break cryptography. They exploit the surrounding interface: malicious browser extensions, clipboard substitution, fake support messages, compromised websites, or deceptive transaction prompts. Trezor’s on-device confirmation creates a second communication channel. The user should compare the recipient address and amount shown on the device with the intended transaction before physically approving it.

    This is a useful mental model: the device protects authorization, not intention. If a smart contract interaction is technically valid but economically dangerous, the hardware may still sign it. Likewise, if a user confirms an attacker’s address after failing to inspect the screen, the physical button becomes confirmation of the mistake rather than a defense against it.

    Trezor’s open-source architecture is another important design choice. Open firmware and hardware designs allow researchers and the wider community to inspect how the system is built. Transparency improves the possibility of finding defects and evaluating claims, although open source is not equivalent to “bug-free.” Security still depends on code quality, update practices, supply-chain integrity, and the user’s operating habits.

    Choosing a device and setting it up safely

    The current Trezor family spans different priorities. The Trezor Model T uses a color touchscreen, which can make entering sensitive information and reviewing prompts more intuitive. The Safe 3 is positioned as a modern mid-range option, while the Safe 5 and Safe 7 serve users who want more premium hardware. Newer models such as the Safe 3, Safe 5, and Safe 7 include EAL6+ certified Secure Element chips designed to strengthen resistance to physical extraction and tampering.

    That specification should be interpreted carefully. A Secure Element can improve protection if an attacker obtains the physical device, but it does not eliminate the importance of the recovery backup. In most realistic loss scenarios, the recovery phrase remains the decisive asset. A stolen device may be replaceable; a leaked or destroyed backup can be far more consequential.

    During setup, the device generates a 12-word or 24-word BIP-39 recovery seed. This seed is not a password and should never be photographed, typed into a website, stored in cloud notes, or sent to support personnel. It is the underlying recovery authority for the wallet. Anyone who obtains it may be able to restore the funds elsewhere, while anyone who loses it may be unable to recover the wallet after device failure or loss.

    Some advanced models, including the Model T and Safe 5, support Shamir Backup. Instead of relying on one complete seed, Shamir Backup divides recovery information into multiple shares, with a required threshold for reconstruction. This can reduce the risk that one misplaced paper reveals the whole wallet. It also introduces an administrative burden: the owner must know where the shares are, how many are required, and how heirs or trusted parties would use them. A sophisticated backup scheme that nobody can reconstruct is not a resilient scheme.

    A passphrase creates a separate hidden wallet derived from the original seed plus the chosen passphrase. It can be valuable when a user wants plausible deniability or an additional barrier if the seed is exposed. The boundary condition is severe: a forgotten passphrase cannot be reset through the recovery seed. The hidden wallet’s funds may become permanently inaccessible. For most users, a simpler and well-tested backup process is safer than adding advanced features without a documented recovery plan.

    Using Trezor Suite without confusing convenience with security

    Trezor Suite is the official companion environment for managing accounts, viewing balances, receiving funds, and sending transactions. The desktop application is available for Windows, macOS, and Linux, alongside a web-based platform. Users seeking the official trezor suite download should verify the source carefully, because fake wallet applications are a recurring threat in cryptocurrency.

    A sensible setup process starts with a clean computer, the manufacturer’s official distribution channel, and verification of the device packaging and prompts. The recovery words should be generated and displayed by the device, not supplied by a website or preprinted on a card. After setup, a small test transaction can confirm that the address, network, and receiving workflow are understood before larger funds are transferred.

    Suite also includes privacy features, including Tor routing. Tor can conceal the user’s IP address from the service handling wallet requests, which is useful because transaction data is public even when a person’s identity is not directly written onto the blockchain. Tor does not make blockchain activity anonymous by itself. Amounts, addresses, timing, exchange records, and other clues can still support analysis.

    Native support is not universal merely because a device advertises broad asset coverage. Trezor devices support more than 7,600 cryptocurrencies across multiple networks, while Suite natively handles important assets such as Bitcoin, Ethereum, Cardano, Dogecoin, and various ERC-20 stablecoins. Some assets, including Bitcoin Gold, Dash, Vertcoin, and Digibyte, have been deprecated in Suite and may require a compatible third-party wallet. Before buying a token, check both device compatibility and the current software path for that specific network.

    Where alternatives fit better

    Ledger is the most obvious comparison for many US buyers. Ledger devices commonly emphasize closed-source secure elements and, on some models, Bluetooth connectivity for mobile use. That can make mobile interaction more convenient, but wireless connectivity creates a different attack surface and a different trust discussion. Trezor’s intentional omission of Bluetooth favors a wired, more limited connection model. Neither choice is universally superior; the relevant question is whether convenience or attack-surface minimization matters more for the user’s routine.

    A software wallet such as MetaMask or Rabby is more flexible for decentralized finance, non-fungible tokens, and frequent smart-contract interactions. It is also more exposed to the browser and operating system. Using one of these interfaces with a Trezor can preserve hardware-based signing while providing broader application compatibility, but the user must still understand what the contract is asking the device to approve. Hardware protection does not turn an unfamiliar protocol into a trustworthy one.

    Exchange custody is simpler for users who prioritize account recovery and frequent trading over direct control. The trade-off is that the exchange controls the keys and can impose withdrawal limits, account freezes, or identity and operational requirements. Self-custody transfers those responsibilities to the individual. Trezor is best understood not as a universal replacement for exchanges or software wallets, but as a tool for users prepared to manage recovery, verification, and transaction review.

    What to watch as the ecosystem develops

    Recent project messaging continues to emphasize open-source security and offline keys. The practical implication is not that users should trust a slogan, but that they should evaluate whether the complete workflow remains inspectable and maintainable: device firmware, desktop software, supported assets, third-party integrations, and recovery procedures. In a rapidly changing ecosystem, support deprecations may matter as much as new features.

    The most useful forward-looking signal is therefore operational consistency. If wallet software expands support for more networks and applications, convenience may improve while transaction interpretation becomes harder. If privacy tools become easier to use, users may gain better network-level privacy without receiving complete anonymity. And if more people adopt advanced backup methods, education about recovery thresholds and inheritance will become as important as the underlying cryptography.

    Frequently asked questions

    Is a Trezor wallet completely safe from hacking?

    No wallet is completely safe. Trezor isolates private keys and requires physical confirmation, which can substantially reduce several online attack paths. However, phishing, fraudulent addresses, malicious smart contracts, stolen recovery phrases, counterfeit software, and careless approval can still lead to loss.

    Can I recover my cryptocurrency if my Trezor device is lost?

    Usually, yes, if the recovery seed was created correctly and stored securely. The wallet can generally be restored on a compatible replacement device. A passphrase-protected hidden wallet requires the exact passphrase as well as the seed, and Shamir Backup requires the necessary number of shares.

    Should I use a passphrase with my Trezor?

    Only if you can manage the additional recovery responsibility. A passphrase can protect a hidden wallet even if the device and seed are compromised, but losing or mistyping it permanently separates you from those funds. Write down a carefully documented recovery plan without exposing the passphrase to unauthorized people.

    Can Trezor be used with DeFi and NFT applications?

    Yes. Trezor can integrate with third-party wallets such as MetaMask, Rabby, Exodus, and MyEtherWallet. The integration expands application access, but it does not remove the need to inspect transaction details and understand the permissions or contract actions being approved.

    The strongest case for a Trezor wallet is not that it makes cryptocurrency effortless. It makes responsibility more visible. The device separates transaction preparation from transaction authorization, while the recovery system forces the owner to plan for loss, theft, and succession. That friction is the feature—but only when the user treats verification and backup as part of the security model rather than as setup chores.

  • Private Keys, Ledger Devices, and the Real Meaning of Secure Crypto Trading

    A hardware wallet can protect a private key from an internet-connected computer, but it cannot protect a careless approval, a copied recovery phrase, or a misleading transaction. That distinction is the starting point for understanding cryptocurrency security. The most important security boundary is not the wallet app’s portfolio screen; it is the moment when a transaction is decoded, reviewed, and physically approved on the device.

    For US users holding Bitcoin, Ethereum, Solana, or a broader collection of digital assets, Ledger devices offer a practical form of self-custody. Their secure-element architecture keeps private keys inside the hardware, while companion software makes balances, staking, swaps, purchases, and decentralized applications easier to manage. Yet convenience creates its own questions. A hardware wallet reduces certain attack surfaces; it does not eliminate operational, social, market, or recovery risks.

    Ledger hardware wallet used as a physical transaction approval boundary for protecting cryptocurrency private keys

    What a hardware wallet actually protects

    A private key is the secret that authorizes control over cryptocurrency. The coins do not sit inside the device itself; they remain recorded on a blockchain. The device stores and uses the cryptographic material needed to sign transactions without exposing that material to the connected computer or phone.

    This is why the common phrase “offline storage” needs refinement. A Ledger device may be connected to a computer while a transaction is prepared, but the private key is designed not to leave the hardware. The computer can propose a transaction, and the device can sign it, but the signing secret remains within the hardware security boundary. Secure-element chips, including models described with EAL5+ or EAL6+ certifications, are intended to make direct extraction substantially more difficult than stealing a key from an ordinary software wallet.

    The protection is therefore asymmetric. Malware on a laptop may be unable to read the private key, but it may still alter the destination address or transaction amount before the request reaches the device. Physical confirmation matters because the device gives the user a second place to inspect what is being authorized. The display is not a decorative feature; it is a final checkpoint between an external application and an irreversible blockchain action.

    That leads to a more accurate mental model: a hardware wallet is not simply a vault. It is a signing instrument with a controlled approval interface. Its value depends on keeping the signing secret isolated and on the user verifying meaningful transaction details before pressing the buttons.

    Ledger Live: useful interface, separate risk layer

    Ledger Live is the official companion application for Ledger hardware wallets such as the Nano S, Nano S Plus, Nano X, Stax, and Flex. It can display portfolios, install blockchain applications, and support transactions across a large range of assets. The platform is available across major desktop and mobile environments, including Windows, macOS, Linux, Android, and iOS, although Apple’s system restrictions can limit some device connections and functions.

    Users can find support for more than 5,500 cryptocurrencies and tokens, including major networks such as BTC, ETH, SOL, XRP, and ADA. That breadth should not be confused with identical functionality. Some assets are not natively managed inside Ledger Live. Monero, for example, may require a compatible third-party wallet. In such cases, the Ledger device can still serve as the signing hardware, but the user must evaluate the additional software and its transaction display carefully.

    For the official companion software and current device-management information, readers can consult ledger. The key security principle remains unchanged regardless of the interface: never enter a recovery phrase into a website, chat window, or computer prompt, and never approve a transaction that has not been checked on the physical device.

    Ledger Live also connects security with activity. Native staking is available for networks such as Ethereum, Solana, Polkadot, and Tezos, while third-party providers can support fiat purchases and sales through services including PayPal, MoonPay, Transak, or Banxa. These integrations may reduce friction, but they introduce counterparties, fees, identity checks, processing delays, and regulatory or availability constraints. A non-custodial wallet does not make every surrounding service non-custodial.

    Crypto trading changes the security equation

    Long-term storage and active trading are different operational problems. A person who rarely moves assets can keep the device disconnected, verify a small number of transactions, and focus on recovery planning. A trader who swaps tokens, uses decentralized finance, or interacts with Web3 applications faces a larger approval surface. More transactions mean more opportunities to misunderstand permissions, sign an unfavorable contract, or overlook a malicious domain.

    WalletConnect and similar protocols can link a Ledger device to decentralized applications while keeping the private keys on the hardware. Transaction details may be shown for review on the Ledger display, and physical confirmation is required for security-sensitive actions such as sending, staking, or swapping. That is a meaningful defense against remote key theft. It is not a guarantee that a smart contract is safe, economically sound, or honest about what the user is approving.

    One subtle risk is the difference between a simple transfer and a contract interaction. A transfer usually presents a recognizable recipient and amount. A decentralized application may request a token approval, a swap, a staking action, or another permission whose consequences are less obvious. The device can authenticate the signature, but the user still needs enough context to understand the contract and the scope of the authorization. Hardware protects the key; it does not perform investment research.

    For active US traders, a sensible separation of duties can help. Keep a larger strategic reserve on a device used rarely, and use a smaller, deliberately funded account for experimental applications or frequent swaps. This does not remove risk, and it may create additional management complexity, but it limits the amount exposed by a single mistaken approval.

    Recovery phrases are the decisive boundary

    The 24-word recovery phrase often receives less attention than the device, even though it can recreate control over the wallet. Anyone who obtains the phrase may be able to move the assets without possessing the original hardware. Conversely, a lost or damaged device may be survivable if the phrase remains accurate, private, and available.

    Store the phrase offline, protect it from unauthorized people, and avoid photographing or typing it into an internet-connected device. A bank safe-deposit arrangement, home fire protection, and inheritance planning may each be relevant depending on the value and the user’s circumstances. The goal is not merely secrecy. It is durable availability without creating a convenient digital copy.

    Ledger Recover is an optional paid, encrypted backup service for the recovery phrase that is tied to identity verification. It may appeal to users who fear losing a handwritten or metal backup, but it changes the threat model. Instead of relying only on personal physical custody, the user accepts an identity-linked recovery process and its associated trust, privacy, and access considerations. There is no universally correct choice: the appropriate method depends on whether the greater concern is accidental loss, third-party exposure, or long-term inheritance.

    Common myths and practical tests

    Myth: A hardware wallet makes phishing harmless

    Reality: phishing can persuade a user to reveal the recovery phrase or approve a transaction. The device cannot compensate for a compromised secret or an unverified signature.

    Myth: A larger asset-support number means universal compatibility

    Reality: support can mean native portfolio display, a device application, or compatibility through external wallet software. Check the exact workflow for each asset before transferring funds.

    Myth: Staking is just passive storage

    Reality: staking involves network rules, validators or service providers, lockups or withdrawal conditions, and possible smart-contract or operational risks. It can be accessed securely through hardware while still carrying financial and technical exposure.

    A reusable decision test is simple: identify what is being protected, identify who or what can still change the transaction, and identify how recovery would work after loss. If the private key is isolated but the user cannot read the transaction, the system is incomplete. If the device is secure but the recovery phrase is copied to cloud storage, the principal defense has been bypassed.

    What to watch as hardware wallets become more connected

    Recent Ledger messaging has emphasized pairing a crypto wallet with its companion app to manage portfolios and access DeFi and Web3 services. That direction reflects a broader tension in self-custody: users want stronger protection without giving up the speed and composability of online markets. If integrations expand, the crucial question will not be whether a wallet supports more applications, but whether users can understand and verify increasingly complex permissions.

    The likely boundary of secure crypto trading will therefore be human-computer interaction. Clearer transaction displays, better permission warnings, transparent third-party integrations, and safer account separation could reduce avoidable mistakes. None should be treated as a substitute for recovery discipline or independent review. Security improves when the system makes the dangerous action harder to misunderstand.

    Frequently asked questions

    Does a Ledger device store my cryptocurrency?

    No. Cryptocurrency balances are recorded on their respective blockchains. The device stores and protects the private keys used to authorize transactions, while companion software reads blockchain data and presents it to the user.

    Can I trade crypto while keeping private keys offline?

    Yes, in the relevant sense. A device can sign transactions for exchanges, swaps, staking, and supported Web3 applications without exporting the private keys. However, online applications can still present malicious or misunderstood transactions, so review on the physical display remains essential.

    Is Ledger Live the only software option?

    No. Ledger devices may work with compatible third-party wallets for assets or functions not natively supported in Ledger Live. Trezor Suite and Trezor hardware wallets are another established hardware-wallet approach. Compare security practices, asset support, recovery design, and usability rather than relying on brand reputation alone.

    The strongest conclusion is also the least glamorous: private-key protection is a system of habits, boundaries, and checks. A Ledger device can keep the signing secret away from ordinary malware, but the user must still secure the recovery phrase, verify the transaction, understand the application, and choose an exposure level appropriate to the activity. Hardware is the foundation of self-custody—not the whole structure.

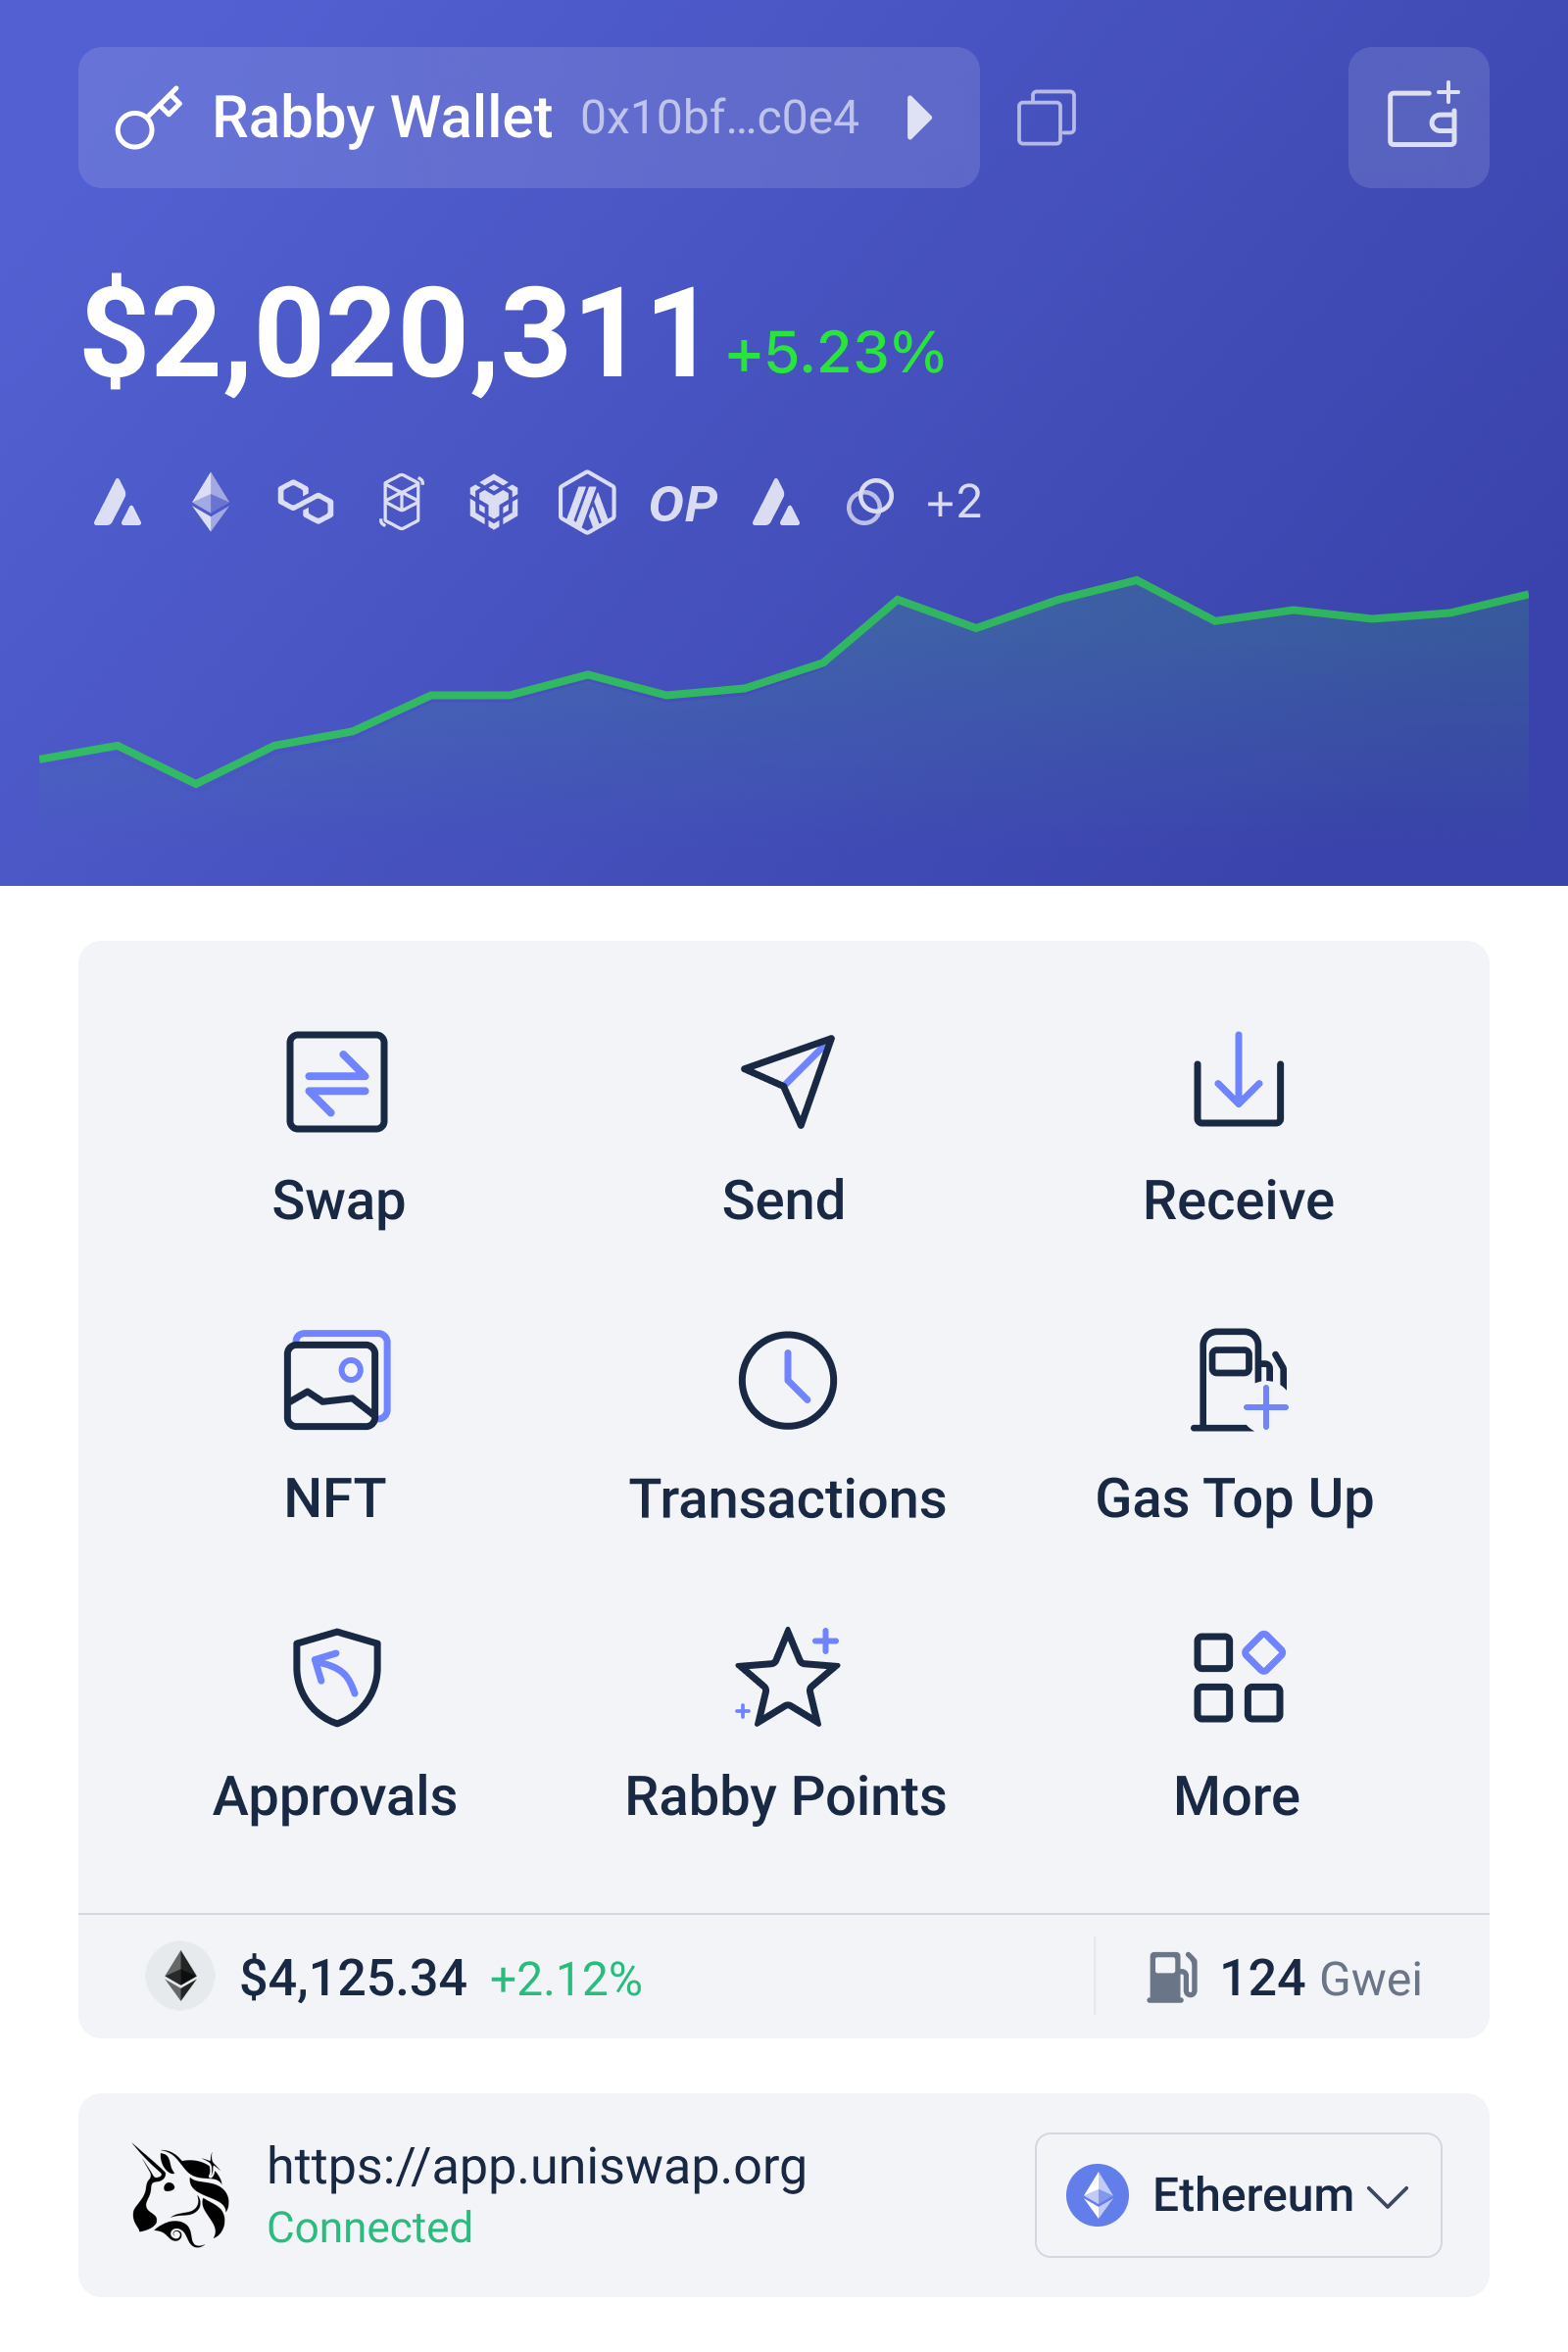
  • The Wallet Is Not the Safety System: What DeFi Users Should Expect from Rabby

    A wallet can warn you about a dangerous transaction and still leave you fully exposed to a bad decision. That is the counterintuitive fact many DeFi users miss. Security is not created by a colorful interface or a “simulation” button; it emerges from how well a wallet translates opaque blockchain actions into consequences a person can inspect before signing.

    Consider a familiar US-based scenario. You connect to a new decentralized exchange, approve a token, and submit a swap that appears ordinary. The transaction succeeds, but the result is not what you expected: the approval was broader than necessary, the received asset was not the token you thought it was, or a contract interaction granted a third party more control than the interface made obvious. Nothing necessarily “broke.” The danger was hidden in the transaction’s meaning.

    Wallet interface illustrating how DeFi transaction details and security warnings can be reviewed before signing

    Myth One: A Web3 Wallet Is Just a Digital Keyring

    The traditional mental model is simple: a wallet stores cryptocurrency. Technically, that is incomplete. Assets remain recorded on blockchains; a wallet manages the cryptographic keys and produces signatures that authorize state changes. When you use a DeFi protocol, the wallet is the boundary between your intention and a smart contract’s execution.

    That boundary matters because a single transaction can contain more than “send this token.” It may call a contract, invoke a function, set an allowance, route an asset through multiple pools, or interact with a protocol deployed across several Ethereum Virtual Machine, or EVM, networks. The human-readable description shown by a decentralized application is useful, but it is not the blockchain’s final authority. The signed transaction is.

    This is where an advanced wallet such as rabby is potentially more valuable than a basic signing tool. Its purpose is not merely to hold keys, but to help users inspect the proposed interaction across EVM chains before approval. The distinction is important: a wallet can improve the quality of a decision without making the decision for you.

    What Transaction Simulation Actually Tells You

    Transaction simulation is best understood as a controlled preview. The wallet attempts to execute the proposed transaction in an environment that reflects the current blockchain state, then reports expected changes such as assets leaving the wallet, assets arriving, or permissions being modified. For a DeFi user, this can turn an unreadable contract call into a more practical question: “What will my address look like if I sign this?”

    That shift from intent to outcome is the technology’s most useful contribution. A swap interface may say that you are trading one asset for another. A simulation can help reveal whether the call appears to produce that outcome, whether an unexpected token is involved, and whether the wallet’s balance or approvals change in a way that deserves scrutiny. In a multi-step protocol interaction, the difference between the displayed promise and the simulated effect can be the earliest warning.

    But simulation is not proof of safety. It is a model of a transaction under particular conditions. Blockchain state can change between simulation and inclusion in a block. A protocol may depend on external prices, liquidity, block timing, oracle updates, or transactions that execute before yours. A malicious contract can also behave differently depending on the caller, block context, or execution path. Simulation therefore reduces some forms of uncertainty; it does not eliminate adversarial behavior or market risk.

    This is the central boundary condition. A warning system can identify a suspicious outcome, but it cannot establish that a protocol will remain solvent, that an asset has legitimate value, or that the economic terms of a trade are favorable. A simulation may show that you will receive the expected token while saying little about whether the token is liquid, redeemable, or governed by trustworthy code.

    Myth Two: “The Transaction Failed” Means “Nothing Happened”

    DeFi users often treat a failed transaction as a harmless event. That assumption is unsafe. A reverted transaction generally does not complete its intended state change, but the attempt may still consume network fees. More importantly, the surrounding workflow may include earlier approvals or separate transactions that did succeed. A failed swap does not automatically reverse a prior token allowance.

    Approvals deserve special attention because they change the permission structure of an address. When you approve a contract to spend a token, you are not sending the asset immediately; you are granting spending authority subject to the allowance. Broad or unlimited approvals can be convenient, but they create a larger exposure if the contract is compromised, upgraded unexpectedly, or used through a malicious interface.

    This is one reason transaction review should be treated as a sequence rather than a single green-light moment. Ask what is being authorized now, what was authorized earlier, and what permission will remain afterward. A wallet that highlights approvals and balance changes can make that sequence more visible, but the user still has to decide whether the permission is proportionate to the intended action.

    DeFi Protocol Risk Does Not Disappear Inside a Better Wallet

    A more informative wallet addresses a specific layer of risk: signing risk. It can help detect mismatches between a user’s expectation and the transaction’s apparent effects. DeFi itself adds several other layers.

    Smart-contract risk concerns bugs, flawed assumptions, upgrade mechanisms, and privileged roles. Economic risk includes slippage, impermanent loss, liquidation, thin liquidity, and oracle failures. Market risk can overwhelm a technically correct transaction if prices move sharply. Operational risk includes phishing sites, counterfeit tokens, compromised devices, and mistakes in chain or address selection. A wallet may assist with some of these problems, especially interface-level deception, while having limited visibility into others.

    The practical lesson is to separate “the transaction looks like I intended” from “the strategy is sensible.” Those are different claims. A lending deposit can be correctly represented and still expose you to liquidation or protocol insolvency. A bridge transaction can show the expected token movement and still depend on a cross-chain system with its own failure modes. Good signing hygiene is necessary, not sufficient.

    A Reusable Review Framework for Advanced Wallet Users

    Before signing a meaningful DeFi transaction, review it through four questions. First, identity: am I on the intended chain, using the intended contract, and interacting with the asset I think I am? Second, effect: what leaves the wallet, what arrives, and what changes in my balances or positions? Third, authority: does this transaction grant an allowance, transfer administrative control, or authorize future spending? Fourth, reversibility: if the protocol behaves badly or the market moves, what can I undo, and what cannot be recovered?

    This framework is more durable than memorizing a list of wallet warnings. It also helps explain why experienced users still lose funds. Familiarity can encourage rapid signing, while sophisticated strategies often involve more contracts, more chains, and more permissions. Complexity increases the number of places where an honest interface can still be misunderstood.

    For US users, there is an additional practical consideration: recordkeeping and operational discipline. Wallet activity may matter for tax reporting, portfolio attribution, and security investigations, even when a transaction is part of a complicated protocol route. A clear review process makes it easier to distinguish a swap from a liquidity position, a deposit from an approval, and a failed attempt from a completed action. It does not replace professional tax or legal advice, but it improves the underlying facts.

    What to Watch as Wallets Become More Interpretive

    The recent positioning of Rabby as a wallet for Ethereum and EVM networks reflects a broader direction in Web3: wallets are becoming interpretation layers rather than passive signature prompts. If users increasingly transact across many EVM chains, the value of chain recognition, contract context, simulation, and permission awareness may rise because the cost of confusion rises with network and protocol complexity.

    The unresolved question is how much interpretation users should trust. A warning engine depends on the quality of the information it can obtain and the assumptions it makes about contracts and state. If users treat a clean simulation as a guarantee, improved tooling could create a new form of overconfidence. The better future is not a wallet that removes judgment, but one that makes judgment more informed and makes uncertainty visible.

    The most defensible conclusion is modest but meaningful: a sophisticated Web3 wallet can move security from blind signing toward evidence-based signing. That is a substantial improvement when the alternative is approving contract calls on the basis of a familiar logo or a rushed pop-up. Yet the final responsibility remains distributed across the wallet, the protocol, the interface, the device, and the person holding the keys.

    Frequently Asked Questions

    Is transaction simulation a guarantee that a DeFi transaction is safe?

    No. Simulation can show expected effects under particular blockchain conditions, such as likely balance changes or permissions. It cannot guarantee that a contract is free of bugs, that an asset has value, that market conditions will remain stable, or that execution will be identical when the transaction is mined.

    Why should I review token approvals separately from swaps?

    An approval grants a contract permission to spend a token, while a swap is an intended exchange. The approval may remain active after the swap succeeds or fails. Reviewing both helps you understand not only what happens immediately, but also what authority the contract retains afterward.

    What is the most useful habit when using a Web3 wallet?

    Compare your intended action with the resulting effects before signing. Verify the chain and contract, inspect assets leaving and entering, check for new permissions, and consider whether the action is reversible. This habit remains useful even when wallet security features are strong.