Whoa! This caught me off guard the first time I saw it in action. NFC hardware that looks like a credit card but holds private keys? Wild. At first glance it seems like a gimmick. But then I used one for a month, and things shifted.
Okay, so check this out—NFC smart cards are neither fully hardware wallets nor just fancy keyrings. They live in the gray area between convenience and cold security. My instinct said they’d be too fragile for real use, but I was wrong in important ways. Initially I thought they’d be slow to adopt, though usage patterns tell a different story.
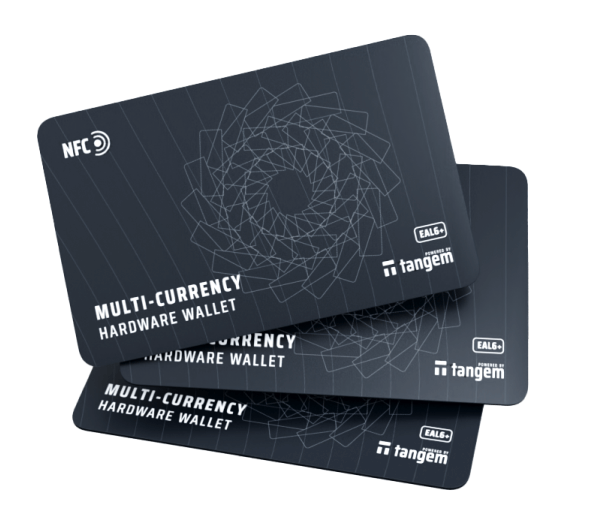
Here’s the thing. NFC cards give you offline private-key storage in a form factor you can carry in your wallet. Simple. No batteries. No USB dongles that break. Sometimes these cards behave like a contactless credit card; other times they act like a sealed vault with strict signing rules. That duality is both liberating and slightly unnerving.
Fast intuition — why people like them
Really? They feel familiar. You don’t need to learn a whole new ritual. Tap, sign, go. For many users somethin’ about that frictionless experience lowers the mental barrier to using cold storage. It’s very very important for mainstream adoption. On the other hand, familiarity invites complacency, which is where design must compensate.
My first impression was: great for daily small-value moves, less so for life-changing sums. Then I thought deeper—actually, wait—let me rephrase that: for many people the right answer is both, depending on how you pair the card with your backup strategy. On one hand the card keeps keys offline; though actually on the other hand you still need secure backup or recovery.
So where does cold storage fit? Cold storage means keeping signing capabilities off internet-connected devices, typically using air-gapped systems. NFC cards often implement secure elements that never expose raw keys, satisfying that core requirement. But they also bridge into hot-wallet territory when the near-field communication interface is used with mobile apps that, if compromised, could lead to mistaken operations—human error matters.
Backup cards vs seed phrases: practical trade-offs
Hmm… seed phrases are battle-tested. They’re simple to copy down, store in a safe, and recover from if everything else fails. But they’re clumsy. Long lists of words are easy to misplace, to mis-transcribe, to accidentally photograph. I’ve seen it. It’s painful to watch. Backup cards, by contrast, can store encrypted backups or be used as multiple redundant signing tokens.
On one side, multiple backup cards can be split and geographically dispersed, creating a flexible multi-location recovery plan. On the other, if you forget passwords or lose all cards, recovery can be impossible without a seeded fallback. Initially this sounded risky to me, but after mapping realistic failure modes I realized redundancy needs methodical thinking, not just optimism.
One practical model I use: keep an NFC primary card for everyday signed transactions, have a secondary backup card stored in a bank safety deposit box, and maintain an encrypted seed or recovery method—ideally split into parts—somewhere else. It’s not foolproof, yet it raises the bar for attackers significantly.
What to ask when choosing a smart-card solution
Check the secure element. Ask about certifications and attestation procedures. Verify whether private keys ever leave the secure chip. If a vendor advertises “air-gapped” signing via QR codes or NFC, test both paths yourself. That hands-on testing will reveal UX flaws and hidden leaks.
Also evaluate the recovery workflow. Is there a documented, tested recovery method that doesn’t rely solely on proprietary cloud services? If the answer is no, walk away or insist on better documentation. I’m biased, but I prefer open standards and clear user stories over shiny marketing.
Finally, think about lifespan. Cards can physically degrade; chips are durable but not immortal. Consider replacing cards every few years and verify export/migration tools before you commit. It bugs me when products skip that conversation entirely…
How NFC cold signing actually works (briefly)
Tap the card to your phone. The wallet app sends a signing request. The secure element prompts you—sometimes with a PIN or a confirmation on the card itself—and produces a signature without revealing the private key. The signed transaction goes back to the app for broadcasting. Simple pipeline, yet many steps require human validation.
Security hinges on two ideas: key isolation and user intent confirmation. If either is broken—say, a compromised app automates confirmations, or a card’s secure element is flawed—the system fails. That’s why independent audits and hardware attestation matter much more than slick UIs. On paper audits look great, though real-world usage tells a fuller story.
One thing I learned sprinting between conferences: when people are rushed they skip checks. People tap and trust. That behavioral risk is where backup cards and clear processes earn their keep.
Where NFC backup cards make the most sense
For people who want tangible backups without writing down dozens of words, backup cards are a smart compromise. They’re especially useful for traveling professionals who need a small, unobtrusive cold storage option in their wallet. For collectors and HODLers with long-term holdings, backup cards add another physical layer that complements vaults and multisig setups.
That said, for ultra-high-value storage I still favor multi-signature hardware wallets distributed across trusted custodians plus cold offline signing devices. No single-card solution should be the only line of defense for a life-changing stash. But for everyday security and middle-weight storage, NFC smart cards are an elegant toolbox addition.
Check this recommendation if you want to dive deeper: tangem wallet has docs and product notes that explain hardware attestation and use cases clearly, and it’s a good starting point for evaluating card-based approaches.
FAQ
Can an NFC card be hacked over the air?
Short answer: extremely unlikely under normal usage. NFC range is very short, and secure elements are designed to never output private keys. Long answer: the risk comes from poisoned mobile apps, social engineering, or physical compromise; protect the phone, vet the app, and use PINs or biometric confirmations when available.
Are backup cards better than seed phrases?
They’re different tools. Seed phrases are universal and resilient if stored properly. Backup cards are convenient, tamper-resistant, and easier to carry, but they require a plan for physical loss and device lifecycle. Best practice: combine approaches—diversify your recovery methods, test periodically, and document the process for trusted heirs or co-signers.
Leave a Reply